Executive News Wire
Fact-first intelligence synthesized across 12+ news agencies. Zero sensationalism.
Live Wire
CHRONOLOGICAL WIRE DISPATCHES
Fact-first intelligence synthesized across 12+ news agencies. Zero sensationalism.
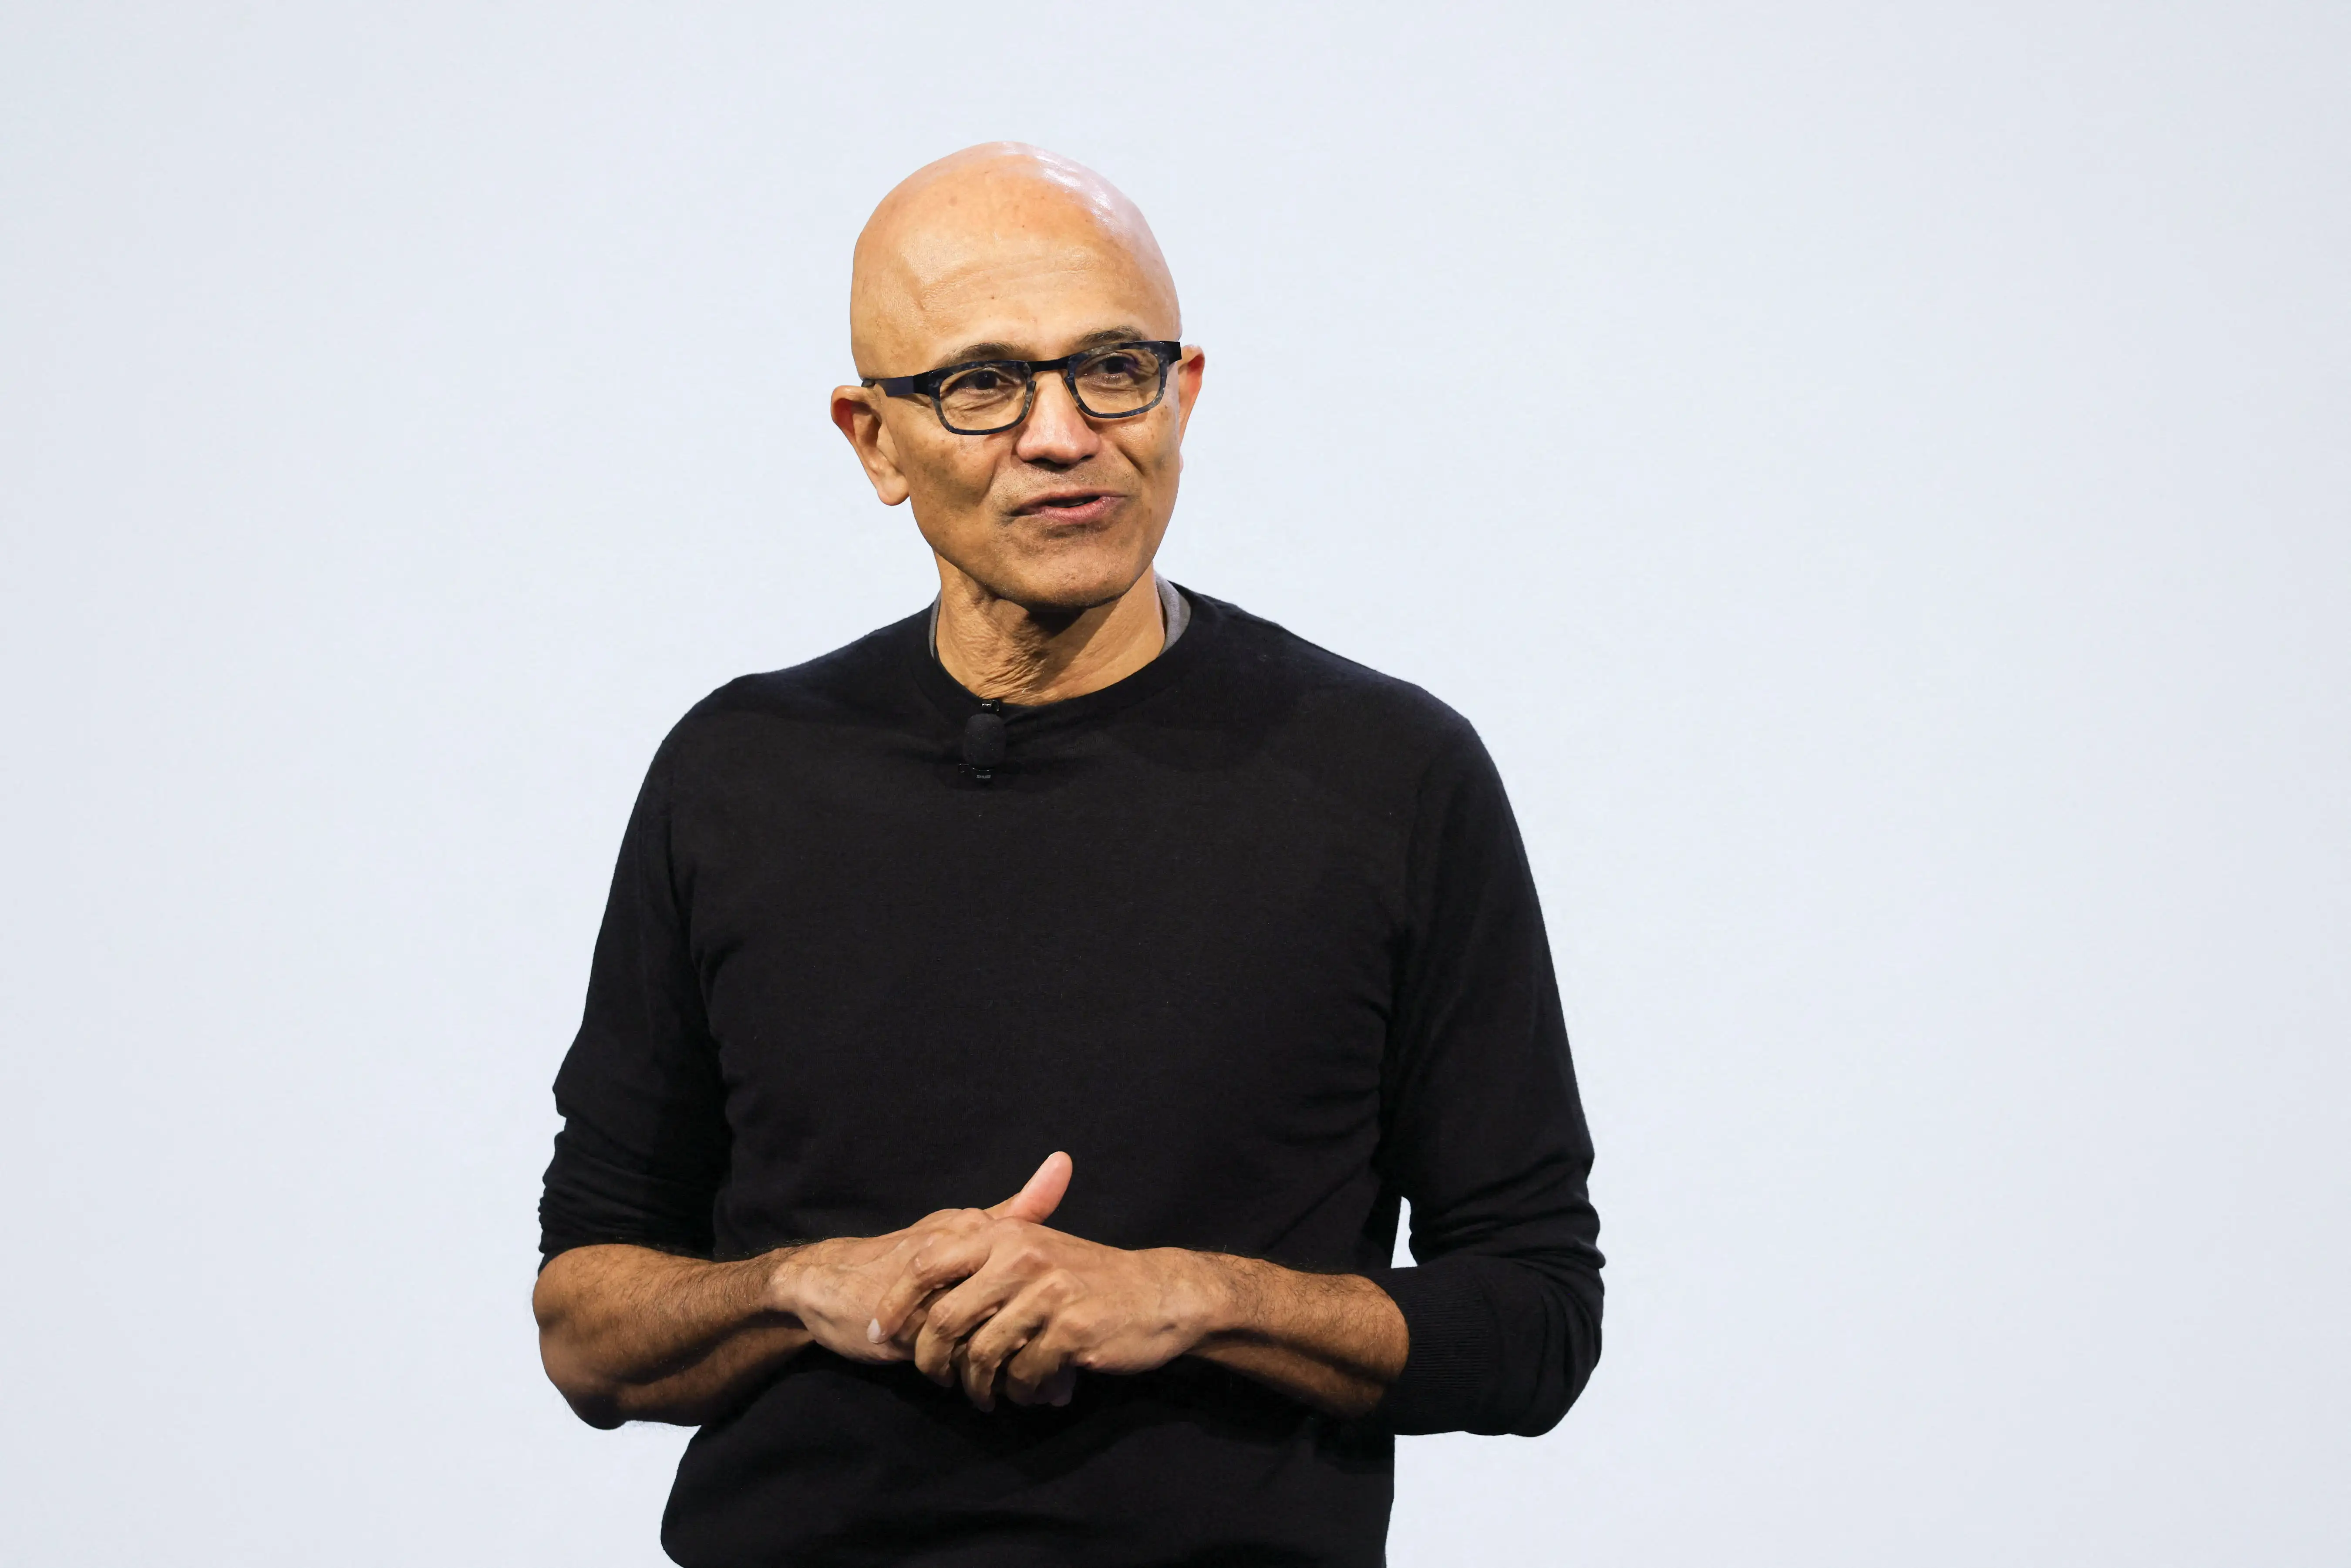
NEW DELHI [NCRBuzz Wire] — ### Architectural Specifications and Hardware Integration
**Microsoft Corporation has released Microsoft Execution Containers, a sandboxing framework designed to restrict autonomous AI agents from performing unauthorized system modifications or data exfiltration.** The security architecture operates directly at the operating system and silicon node interface, isolating active LLM parameters from local file systems, memory registries, and external network sockets.
### Enterprise Deployment and Industry Partnerships
**Major foundational model developers, including OpenAI, Anthropic, and NVIDIA, have confirmed integration plans for Microsoft Execution Containers across their upcoming developer toolkits and enterprise offerings.** According to Pavan Davuluri, executive vice president for Windows and devices, the collaboration aims to mitigate potential Common Vulnerabilities and Exposures (CVEs) related to prompt injection and unauthorized execution loops in local AI workloads.
| Metric / Aspect | Details |
|---|---|
|
| Technology | Microsoft Execution Containers |
| Target Architecture | Desktop and Laptop Client Machines |
| Key Industry Partners | OpenAI, Anthropic, NVIDIA |
| Executive Lead | Pavan Davuluri (EVP, Windows and Devices) |
| Primary Security Goal | Prevent unauthorized agent actions and data leaks |
As generative AI shifts from cloud-hosted APIs to local client execution on NPU-equipped Windows and Apple silicon hardware, safeguarding user data against prompt injections and autonomous agent vulnerabilities has become a primary cybersecurity concern for enterprise software vendors.
Get Instant Delhi-NCR Breaking Alerts on WhatsApp
Traffic advisories, AQI alerts, Metro disruptions, and verified local civic updates. No spam.
You have reviewed or dismissed all fresh dispatches.